Use Cases
Know where your Security Operations Center stands today — and where it needs to go. Our structured assessment gives you an independent, evidence-based view of your SOC's strengths, gaps, and a clear roadmap for improvement.
Services Features
🚨 Built on SOC-CMM — the industry-standard model for SOC excellence
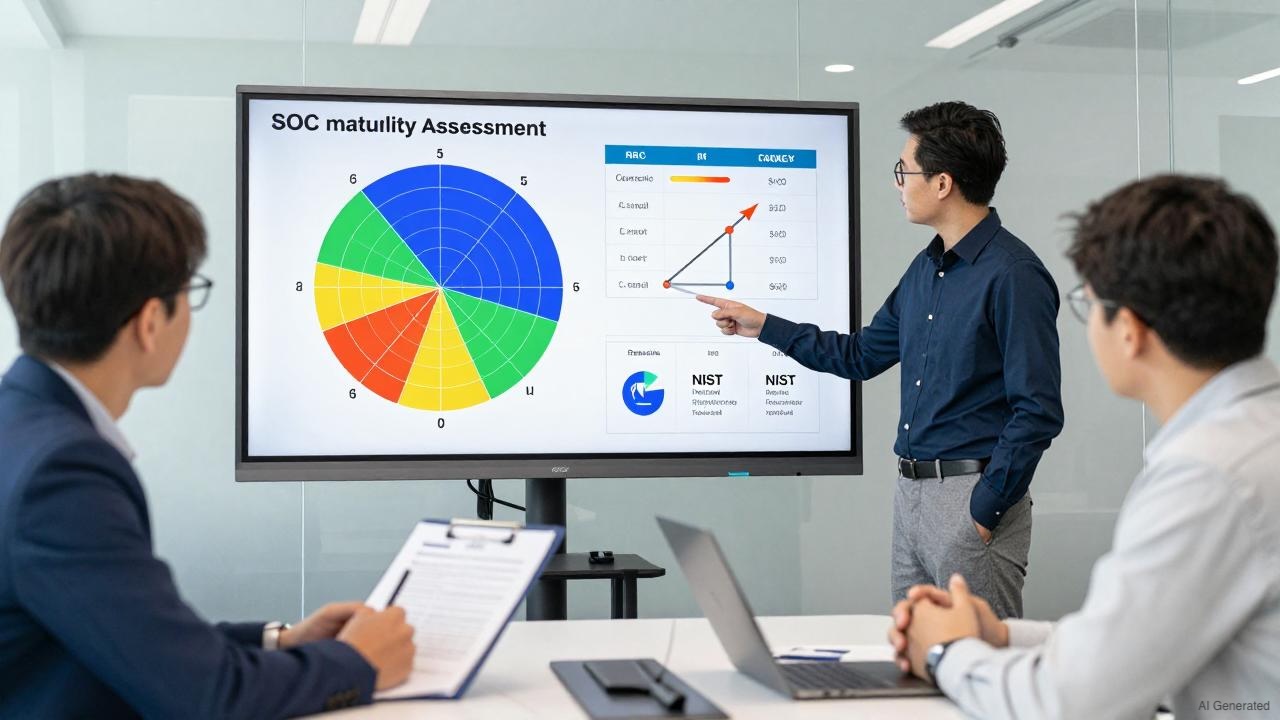
We use the SOC Capability Maturity Model (SOC-CMM), a globally recognized open framework designed specifically for Security Operations Centers. It evaluates maturity and capability across five domains and 26 aspects, providing a structured, objective, and repeatable measure of SOC performance — aligned with the NIST Cybersecurity Framework.
- Business Governance, strategy, and organizational alignment
- People Skills, roles, staffing, and training
- Process Detection, triage, response, and escalation procedures
- Technology Tooling, integrations, and automation
- Services Detection and response service delivery
A clear, six-level scoring model
Each domain is scored on a maturity scale from 0 to 5, from ad hoc and undocumented operations up to a fully optimizing, continuously improving SOC. Capability dimensions are scored separately on a 0–3 scale for technology and services.
0Non-existent > 1Initial / informal > 2Defined / documented > Y3Managed / measured > 4Quantitatively managed > 5Optimizing
🛡️ Designed for SOC operators and service providers alike
Organizations with an internal SOC
- Benchmark your SOC against industry peers
- Justify security investments to leadership
- Prioritize improvement initiatives
- Demonstrate continuous improvement to stakeholders
MSSPs & MDR providers
- Validate and differentiate your service quality
- Identify gaps before clients do
- Build a structured service improvement roadmap
- Demonstrate maturity to prospects and auditors
💡Actionable insight, not just a score
- An independent maturity score across all five SOC-CMM domains and 26 aspects
- A benchmarked view of where you stand relative to industry best practices and peer organizations
- Identification of your SOC's critical strengths and highest-priority gaps
- Tailored recommendations across people, process, and technology with phased quick wins and long-term initiatives
- A NIST CSF mapping of your results for compliance and governance alignment
- An executive-ready report to communicate findings to leadership and stakeholders

Our team will assess your environment and define the right approach