🎯 Use Cases
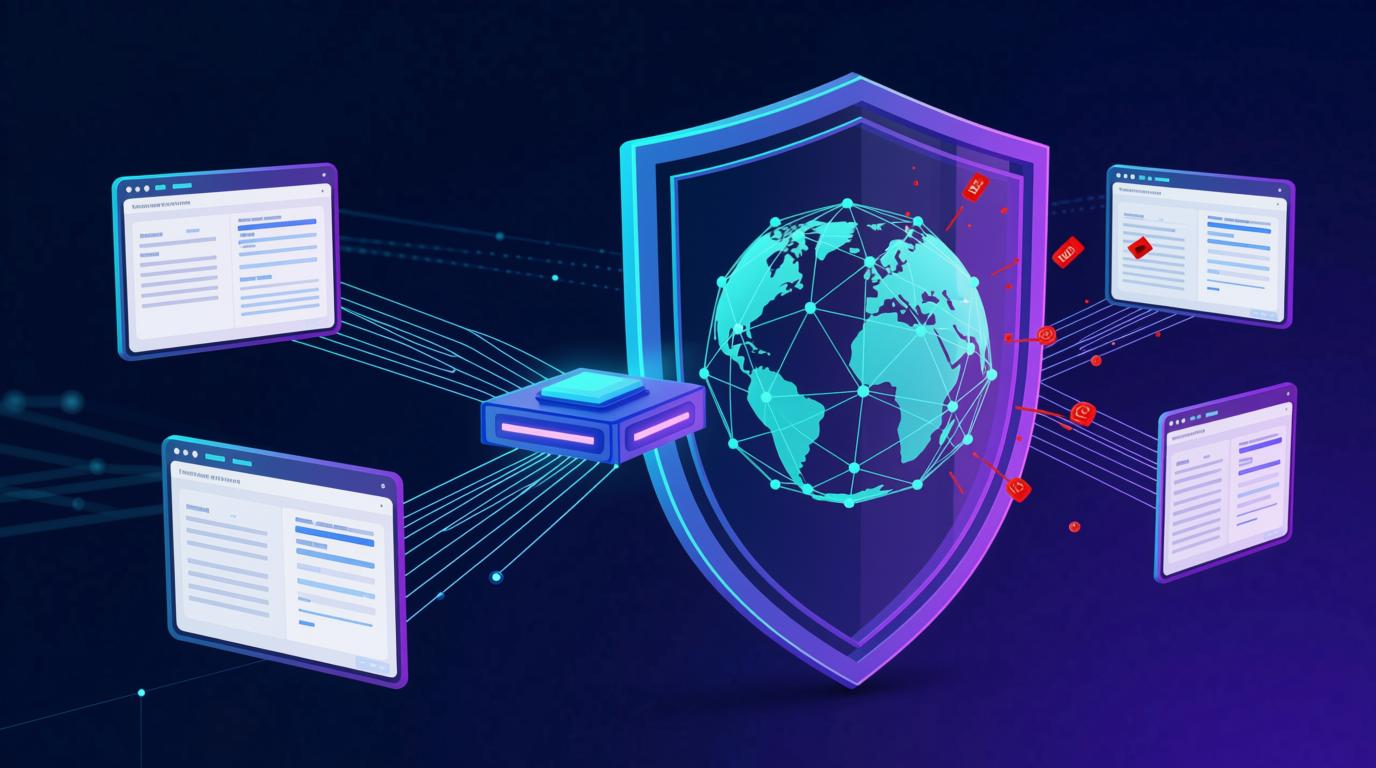
The solution covers the full application security spectrum — from defending customer-facing web apps and APIs against OWASP Top 10 (WAF), DDoS, and bot attacks, to securing LLM-powered applications and agentic AI pipelines against prompt injection, data leakage, and model manipulation. It addresses the needs of enterprises scaling Cloud Native Applications and AI adoption while maintaining compliance and data sovereignty across cloud and on-premises environments.
🛠️ Solution Features
Application & API Security
- Market-leading WAF protecting web apps against OWASP Top 10, zero-days, and volumetric attacks
- Advanced API security, bot management, and DDoS protection across cloud, on-premises, and hybrid
- Real-time BOLA (Broken Object Level Authorization) detection and response for API abuse
AI Security Fabric
- LLM runtime monitoring detecting prompt injection, jailbreaking, system prompt leakage, and model denial-of-service in real time
- RAG Security scanning, classifying, and encrypting enterprise data before it enters AI pipelines — preventing knowledge bases from becoming leakage vectors
- MCP Security Gateway — governing every agent-model-data exchange with end-to-end runtime access control
Cloud Native Application/Workload Protection
- CNAPP platform with leading CWPP capabilities covering runtime protection for containers, Kubernetes, VMs, and serverless functions, with vulnerability management, compliance monitoring, and forensics across AWS, Azure, and GCP.
- Integrates with CI/CD pipelines to enable DevSecOps practices, automating security controls and reducing the risk of vulnerabilities reaching production.
- Unified threat detection and response across containers, Kubernetes, and cloud-native workloads — purpose-built for hybrid environments, giving teams a complete real-time view of risk wherever workloads are running.
In this page:

Ready to get started?
Our team will assess your environment and define the right approach